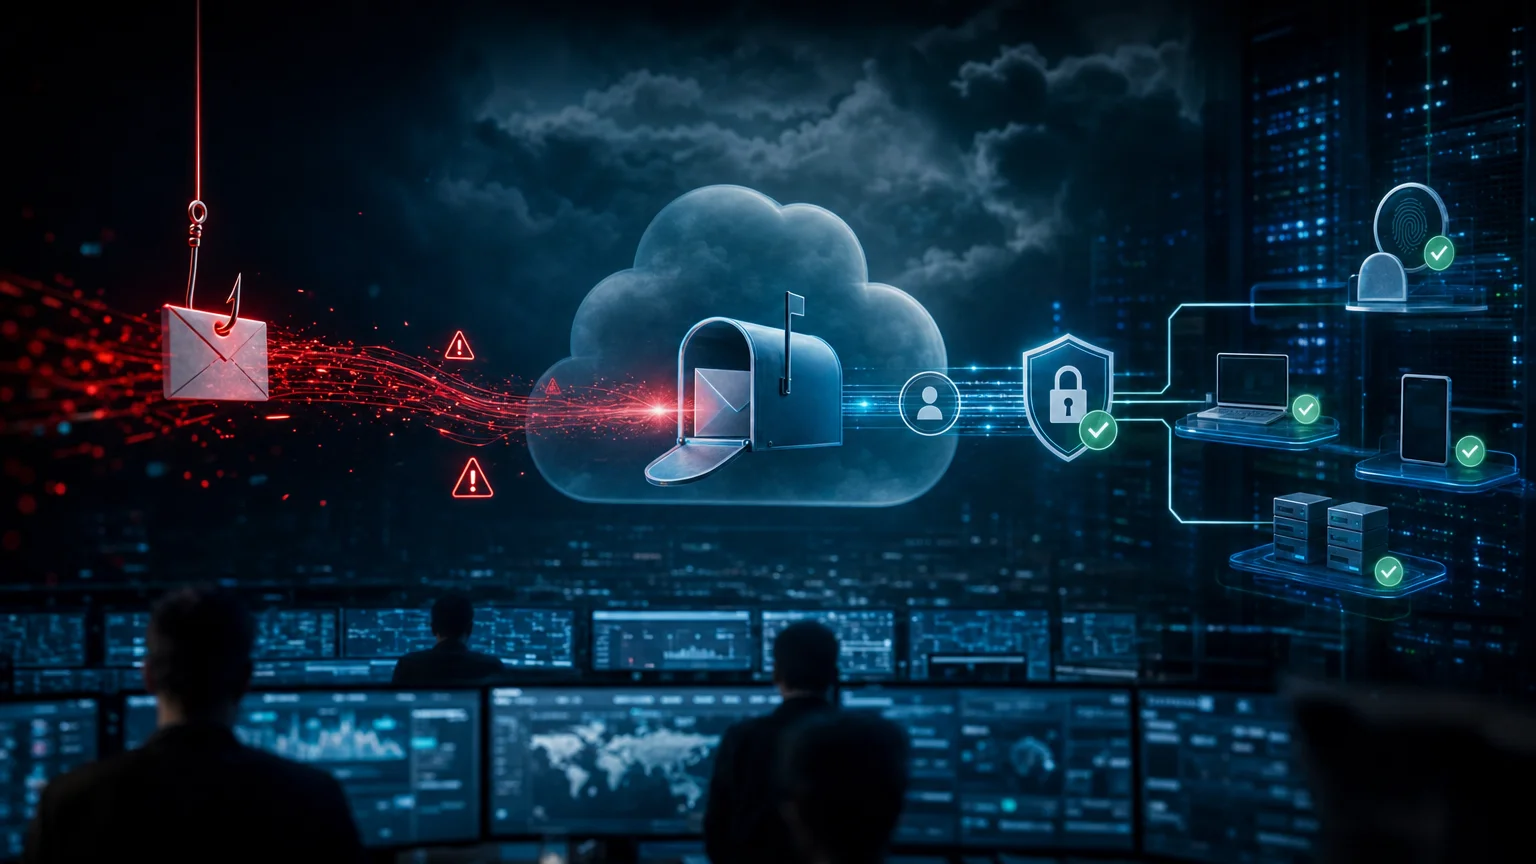
Phishing defense in Microsoft 365 is not limited to filtering messages. A resilient program joins identity protections, mailbox protections, spoofing controls, and an investigation process that can determine who else received a suspicious message.
Microsoft’s guidance addresses phishing-resistant multifactor authentication (MFA), anti-phishing policy tuning in Microsoft Defender for Office 365, spoofing-related controls, and use of Office 365 Threat Intelligence during phishing investigations.
Start with identity: make phishing-resistant MFA the baseline
Microsoft recommends deploying phishing-resistant MFA as the baseline for identity security. For privileged roles in Microsoft Entra ID, Microsoft specifically recommends enforcing phishing-resistant MFA to significantly reduce the risk of account compromise.
Microsoft’s identity guidance identifies phishing-resistant MFA and stronger protection for privileged roles as defensive priorities. More broadly, Microsoft describes MFA as a good way to prevent compromised accounts. Email controls can reduce phishing exposure, while MFA is an important identity safeguard when a malicious message reaches a user.
Configure and tune anti-phishing protection
Microsoft recommends configuring anti-phishing policies in Microsoft Defender for Office 365. Its tuning guidance states that organizations can temporarily increase the phishing email threshold in the policy from Standard to Aggressive, More aggressive, or Most aggressive.
HimalCyberX operational guidance, derived from Microsoft’s tuning material, is to treat a threshold adjustment as a controlled validation activity. Define the purpose of the change, monitor its effect in the organization’s environment, and use the results to decide whether the protection setting remains appropriate. Microsoft’s guidance calls on organizations to use best practices to reduce future phishing risk and validate protection settings.
Microsoft’s guidance does not quantify the impact of individual threshold levels. Organizations should evaluate settings in the context of their mail flow, business tolerance, and incident-handling capability.
Reduce spoofing opportunities in the mail path
Microsoft has published additional resources on setting up mail flow rules, enforcing spoof protections, and configuring third-party connectors to help prevent spoofed phishing messages from reaching user inboxes.
Routing and configuration weaknesses can contribute to spoofing exposure. Organizations can use the relevant Microsoft resources when reviewing mail flow rules, spoof protections, and third-party connector configuration.
Use phishing investigations to identify broader exposure
A reported phishing email may be a wider campaign rather than an isolated event. If an organization has Microsoft Defender for Office 365, either included in a subscription or available as an add-on subscription, it can use Office 365 Threat Intelligence to identify other users who also received the phishing message.
After confirming a phishing message, identifying whether other recipients received it can help teams assess the scope of the message and prioritize follow-up activities. Organizations should apply their approved procedures for triage, containment, communications, and recovery.
Build a validation cycle around the controls
Microsoft’s tuning guidance calls on organizations to use best practices to reduce future phishing risk and validate protection settings. The following is HimalCyberX operational guidance derived from that material for organizing recurring validation:
Set an identity baseline: prioritize phishing-resistant MFA, with particular focus on privileged roles in Microsoft Entra ID.
Review anti-phishing policy posture: configure anti-phishing policies and use temporary threshold tuning where appropriate.
Examine spoofing-related exposure: include mail flow rules, spoof protections, and third-party connector configuration in the review.
Operationalize investigation: where available, use Office 365 Threat Intelligence to look for other recipients of a phishing message.
Validate and refine: periodically review whether protection settings continue to meet the organization’s needs.
These priorities do not eliminate phishing risk. They provide an approach for reducing Microsoft 365 phishing and account-compromise risk by aligning identity controls, email protections, and investigation practices with documented Microsoft guidance.
Related reading
For additional context on the connection between phishing and credential risk, see How phishing raises Microsoft 365 credential risk—and how organizations can respond.
References
Azure identity management and access control best practices — Microsoft
Tune anti-phishing protection - Microsoft Defender for Office 365 — Microsoft
Phishing actors exploit complex routing and misconfigurations to ... — Microsoft
Key Takeaways
Deploy phishing-resistant MFA as the identity-security baseline, with enforcement for privileged Microsoft Entra ID roles as a priority.
Configure Microsoft Defender for Office 365 anti-phishing policies and validate temporary changes to phishing email thresholds.
Review mail flow rules, spoof protections, and third-party connectors as part of phishing-defense planning.
Use Office 365 Threat Intelligence, where available with Microsoft Defender for Office 365, to identify other recipients of a phishing message.
Use a recurring validation process across identity, email protection, and investigation workflows.